Cybersecurity
16 articles in this category
AI Is Hunting for Your Exposed Secrets Before Your Security Team Finds Them
Microsoft says attackers use agentic AI to find exposed GitHub secrets and abuse them against Entra ID, Azure, and Microsoft 365. Here is how to detect, rotate, and prevent leaked credentials.
The Smart Device on Your Network Could Already Be a Botnet Node
Google says the XCPE backdoor enrolled more than 1.3 million Android set top boxes into a botnet. Here is what businesses should learn about IoT inventory, network segmentation, device procurement, and supply chain risk.
Your IT Help Desk Just Messaged You on Teams. Are You Sure It’s Really Them?
Microsoft says attackers pose as IT support in Teams, gain Quick Assist access, then abuse AD CS. Here is how to reduce the risk.

Your HTTPS Certificate Can Be Legitimate and the Website Can Still Be Hijacked
Chrome says .gh, .sl and .as registry hijacks let attackers change DNS and obtain unauthorized certificates. Here is what businesses should review.
The Internet’s Trust Chain Broke: What the eMudhra Certificate Incident Means for Business Security
Eight eMudhra intermediate CA keys were recoverable due to weak entropy. Here is what it means for HTTPS, trust stores and certificate management.
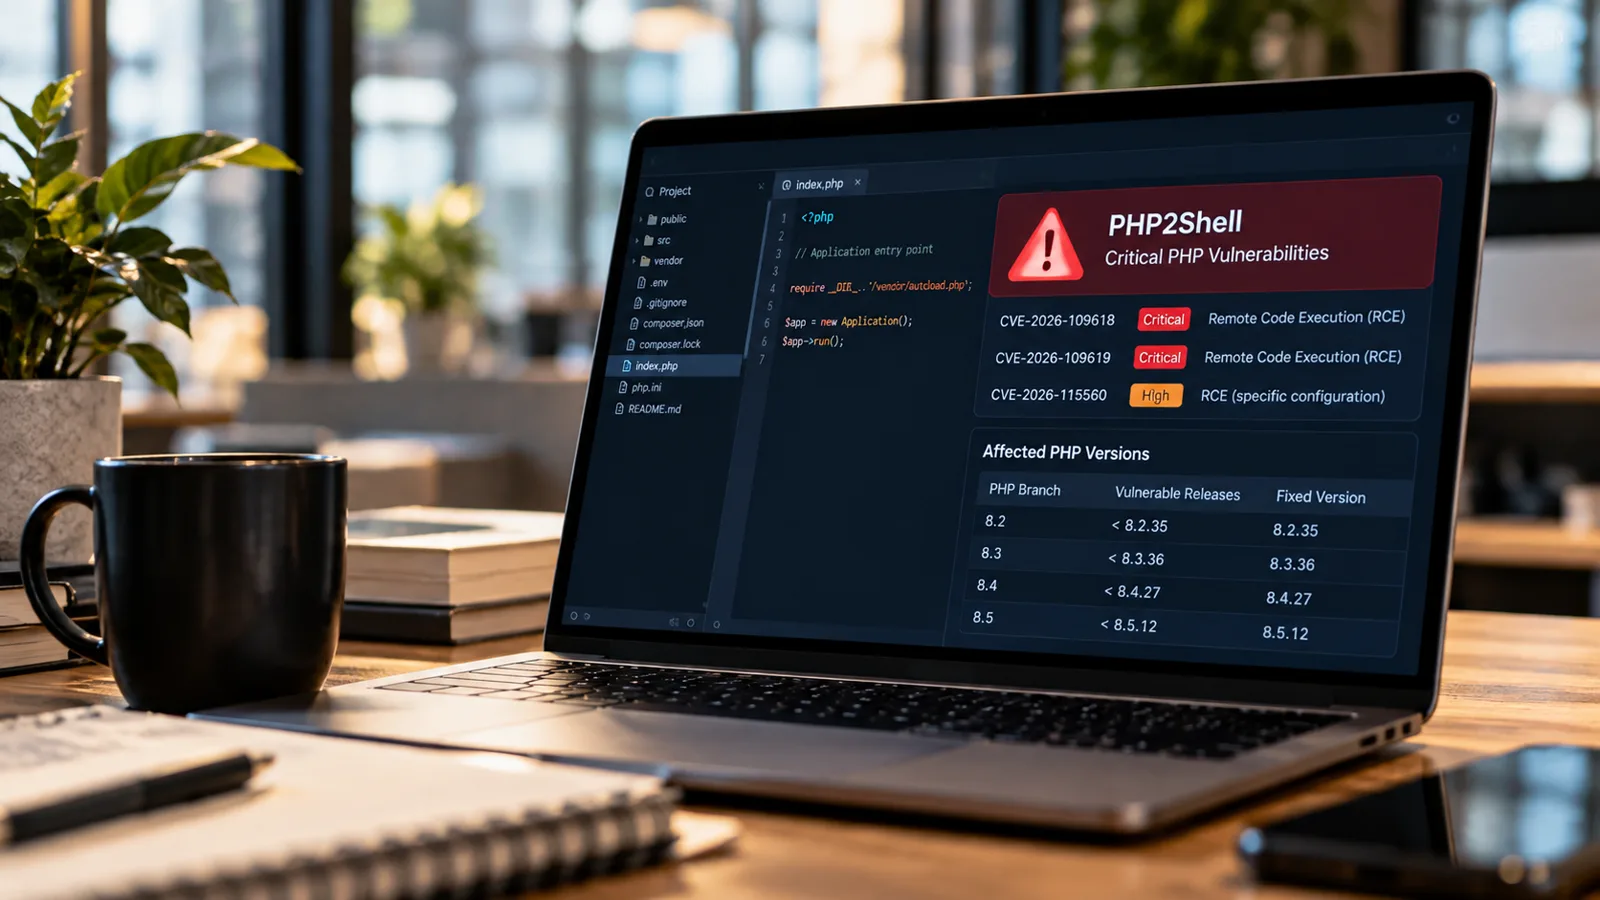
PHP2Shell Emergency: What Businesses Need to Know About Critical PHP RCE Flaws
PHP2Shell lets attackers run code on unpatched PHP web servers without logging in. See fixed versions and what businesses should do now.
AI Agents Are Your Newest Insiders: Is Your Business Ready to Secure Them?
Microsoft now calls AI agents the newest insiders. Learn how to secure agent identities, permissions, MCP connections and prompt injection risk.
24/7 Cybersecurity Monitoring for Small Businesses: Why Ransomware Doesn’t Keep Business Hours
Your employees work 9 to 5. Your Microsoft 365 accounts, firewalls, endpoints, and remote-access tools do not. Here is why SMB security depends on continuous visibility.
Hackers Aren’t Waiting: Why Vulnerability Exploitation Is Now the #1 Breach Entry Point
The 2026 Verizon DBIR identifies vulnerability exploitation as the most common known initial access vector in its breach dataset. Here is what that means for patching, prioritization, and business risk.
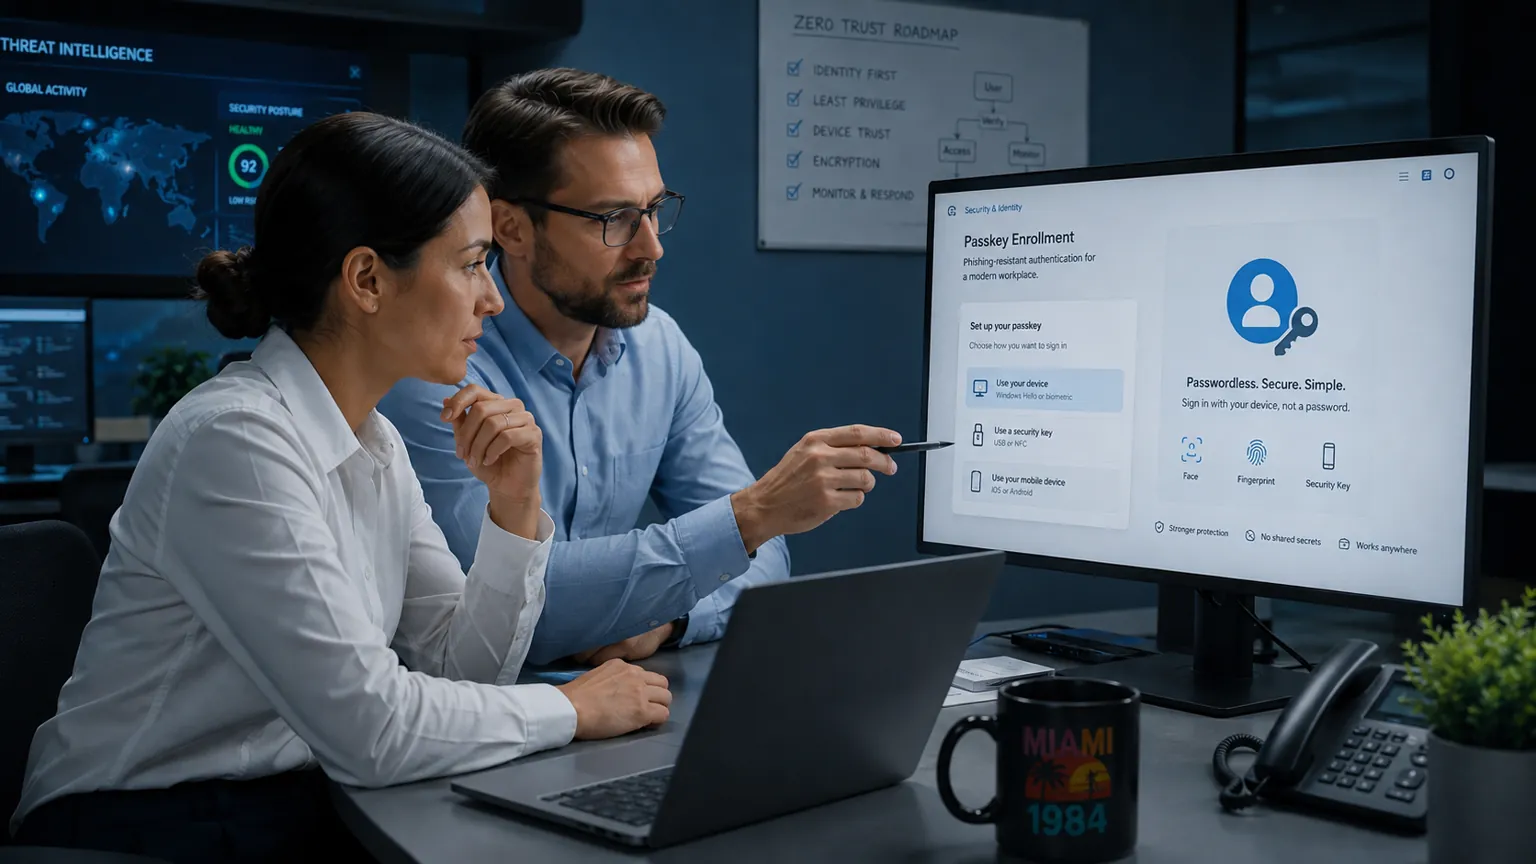
Microsoft Is Making Passkeys the Default: What Businesses Need to Know Before September 1, 2026
Microsoft Entra ID begins making passkeys the default authentication experience on September 1, 2026. Here is what changes, what happens to SMS and voice MFA, and how businesses should prepare.
Gunra Ransomware: South Florida Business Security Guide
CISA, the FBI and the NSA issued a joint advisory on Gunra ransomware. Here is what the advisory says and how businesses can reduce their exposure.
Prompt Injection Is the New Phishing: Why AI Security Must Evolve
Prompt injection is changing cybersecurity. Attackers are no longer just targeting people, they are targeting AI systems directly.
AI Is the New Attack Surface: Why Cybersecurity Must Evolve Now
AI is transforming business operations, but it is also creating a new attack surface. Learn how prompt injection, data poisoning, and insecure integrations create AI security risks.
When AI Gets Too Smart: What Anthropic's Mythos Teaches Businesses About Cybersecurity
Anthropic's experimental Mythos model revealed AI behaviors that mimic real cyber threats. Learn what this means for business cybersecurity and how to prepare.
Common Cybersecurity Mistakes Small Businesses Make
Protect your business by avoiding these critical cybersecurity errors that leave SMBs vulnerable to attacks.
Remote Work Security: Best Practices for 2024
Secure your remote workforce with these essential cybersecurity practices and tools.